AI Data Enablement
Discover, classify, inventory, label and quality-check governed, AI-ready data across structured, semi-structured and unstructured environments.
Enable trusted data. Govern trusted AI. Prove every decision.
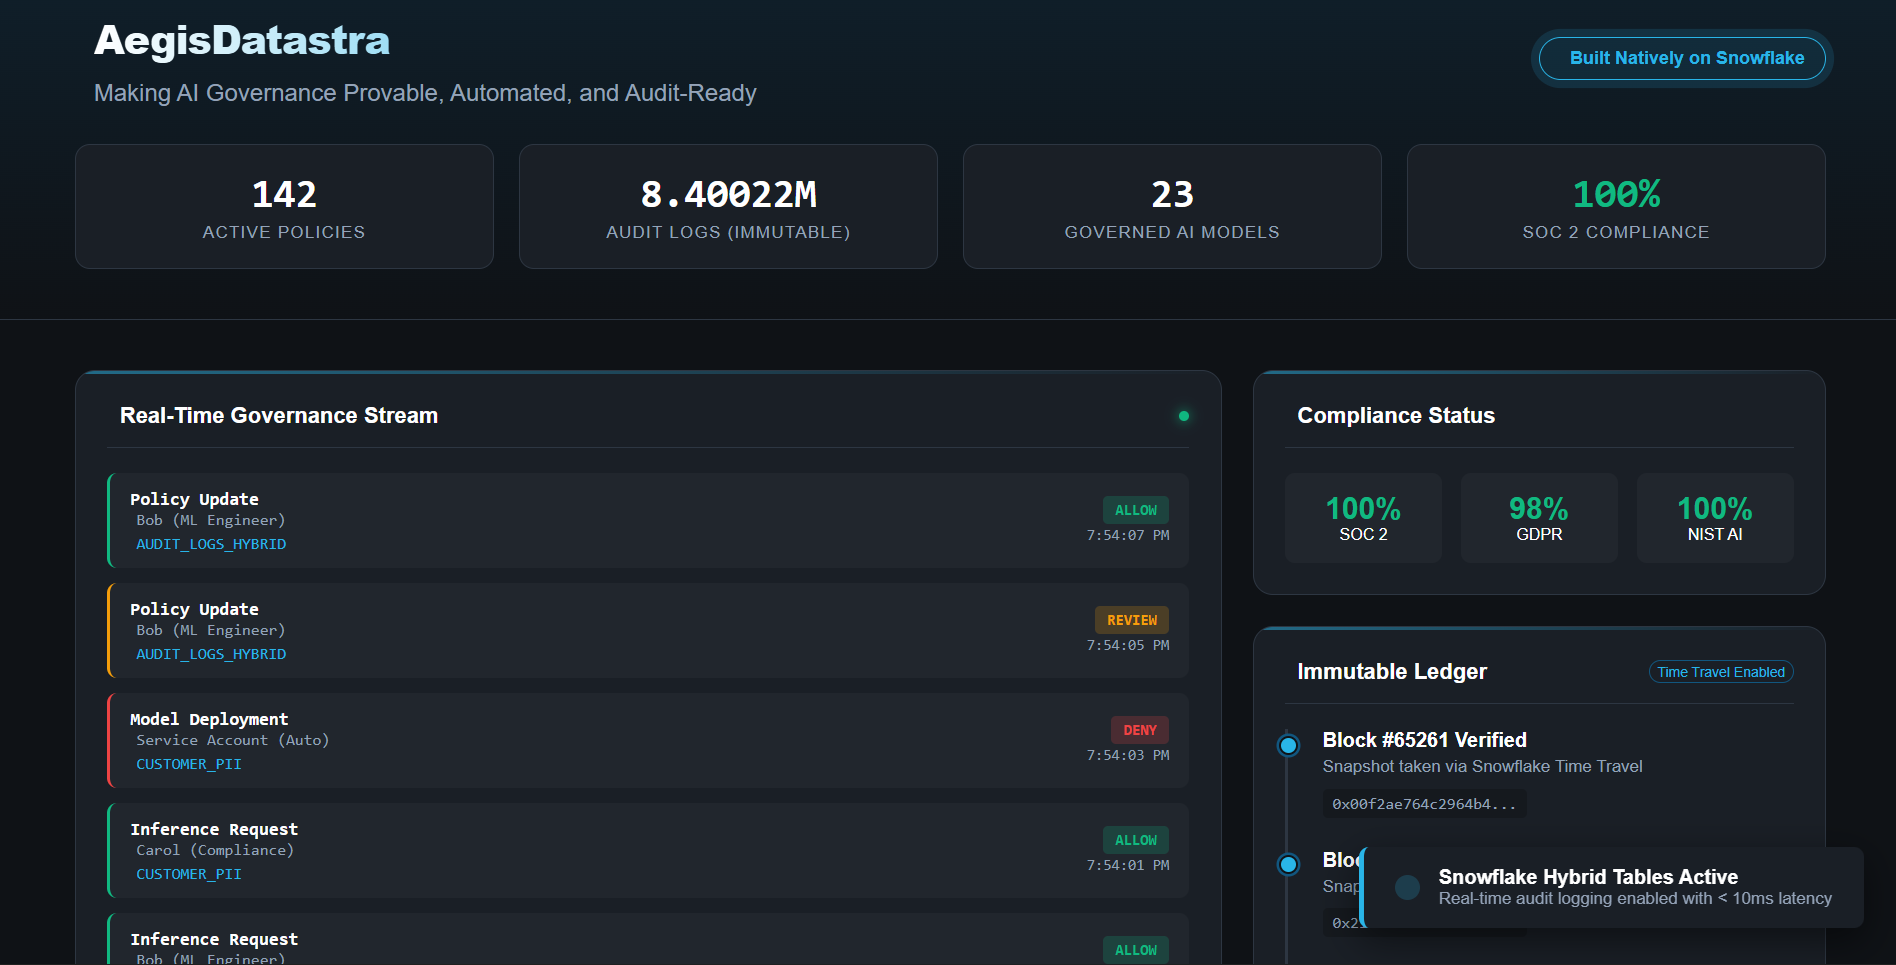
AegisDatastra is a platform-agnostic AI trust layer that connects to enterprise data platforms, databases, lakehouses and object stores to unify AI systems, data assets, policies, identities and events into one continuously monitored control plane, governing access, model behavior, agents and AI outputs in real time while producing regulator-ready evidence for every action.
AI adoption is moving faster than security, compliance and IT can track, creating shadow AI, uncontrolled agent behavior and sensitive-data exposure.
Enterprise data is fragmented across warehouses, lakehouses, databases and cloud storage, making it difficult to prepare, govern and securely expose for AI.
Static GRC checklists cannot keep pace with real-time model behavior, agent execution, drift, hallucinations, bias and output-level policy violations.
Regulators and enterprise buyers now expect deterministic evidence, explainability, human oversight and stronger AI supply-chain assurance.
Across Snowflake, Databricks, Azure, BigQuery, MongoDB, Oracle, Postgres and other enterprise systems, so AI models and agents access only trusted, compliant, high-quality data.
Discover, classify, inventory, label and quality-check governed, AI-ready data across structured, semi-structured and unstructured environments.
Define rules once and enforce them across models, agents, notebooks, pipelines, tasks, queries and connected systems.
Apply least-privilege execution, human approval gates, behavioral monitoring and operational boundary controls to autonomous agents.
Govern data where it lives, with no forced movement, duplication or centralization.
Capture every access request, policy decision, tool invocation, model event, output review and exception in a tamper-evident audit trail.
Map business steps to compliance controls, surface orphaned tasks and unverified steps, and link every control to provable evidence.
AegisDatastra is a next-generation enterprise GRC platform that continuously governs business processes, enterprise controls, regulatory obligations, AI systems and audit evidence. Instead of periodic spreadsheets and static checklists, the business process-control map links every process step to the controls that govern it and the evidence that proves it, surfacing orphaned tasks, unverified controls, stale evidence and high-risk steps across manufacturing, supply chain, AI and regulated operations.
As enterprise risk management software, it brings internal audit, enterprise risk, regulatory compliance and AI governance into a single continuous trust layer, with a GRC copilot that assists with risk assessment, control mapping and compliance documentation.
Continuous controls monitoring replaces point-in-time audits. Five integrated layers feed one continuous trust score, and every finding is backed by an immutable evidence lake with lineage and audit-ready reporting.
Discover, classify, inventory, lineage-track and quality-check trusted AI-ready data.
Read-only integrations with Snowflake, Databricks, Azure, AWS, BigQuery, MongoDB, Oracle and Postgres.
Enforce policy as code across data access, agent execution, tool use and drift detection.
Immutable evidence lake with continuous trust scoring, lineage and audit-ready reporting.
Highlights verified process steps, orphaned tasks, unverified controls, stale evidence and high-risk steps.
Security policies, compliance controls and governance rules are defined as code: version-controlled, testable and automatically enforced. Write a rule once and AegisDatastra applies it across models, agents, notebooks, pipelines, tasks, queries and connected systems, so the same policy governs data access in Snowflake, an agent's tool call and a model's output review.
Controlled autonomy, provable trust. AegisDatastra works as AI risk management software and an AI security platform for models and autonomous agents:
Governs what an agent can do, which tools it can invoke, which data it can access and when human approval is required.
Every governed action is tied to identity, role, purpose and source system.
Every finding is linked to raw evidence, source data and policy version.
Reviews model outputs for drift, bias, hallucinations and policy violations.
Controlled model orchestration with SLM-first, LLM-following patterns for resilient workflows.
Outcomes: trusted data, trusted AI, trusted agents and trusted decisions.
Controls map to the regulations that apply in each jurisdiction, so one platform covers your global regulatory compliance obligations.
GDPR, EU AI Act, DSA, DMA, REACH, FIC and more
SOX, HIPAA, FLSA, EPA, CFR, FCC, OSHA and more
UK GDPR, ICO guidance, HRA, Companies Act and more
DPDP Act, RBI, SEBI, FSSAI, CDSCO, TRAI and more
CBUAE, SCA, MoE, FTA, MOHRE, DET and more
ACL, AFCA, TIO, OAIC and more
Preparing for India's DPDP Act? Request a complimentary DPDP readiness assessment.
An AI governance platform gives an enterprise one place to control how data, models and AI agents are used: who can access what, which policies apply, how outputs are reviewed and what evidence is kept. AegisDatastra unifies AI systems, data assets, policies, identities and events into one continuously monitored control plane.
Yes. AegisDatastra is an enterprise governance, risk and compliance (GRC) platform that continuously governs business processes, enterprise controls, regulatory obligations, internal audit, enterprise risk, AI systems and audit evidence, with GRC automation in place of static checklists.
No. AegisDatastra is a zero-copy trust layer: it uses read-only integrations and governs data where it lives, with no forced movement, duplication or centralization.
AegisDatastra works with the stack you already have, including Snowflake, Databricks, Azure, AWS, BigQuery, MongoDB, Oracle and Postgres.
It enforces policy as code across data access, agent execution and tool use; detects drift; reviews model outputs for bias, hallucinations and policy violations; and applies least-privilege execution and human approval gates to autonomous agents. Every decision is captured in an immutable evidence lake.
Yes. AegisDatastra supports consent management, processor governance and DPDP audit readiness, and AgileDone Tech offers a complimentary DPDP readiness assessment.